CyberDefenders Blog
Dive into the world of cybersecurity with CyberDefenders Blogs. Explore informative articles, insights, and expert perspectives on the latest trends, best practices, and cutting-edge technologies in the field. Stay updated, enhance your knowledge, and empower yourself to defend against cyber threats.
Hands-On Labs vs. Video Courses: Which Actually Builds SOC Skills?
An analyst on your team finishes a 40-hour video course on incident response. They pass every quiz, and the completion certificate lands in your inbox. Two weeks later a real alert fires, a PowerSh...
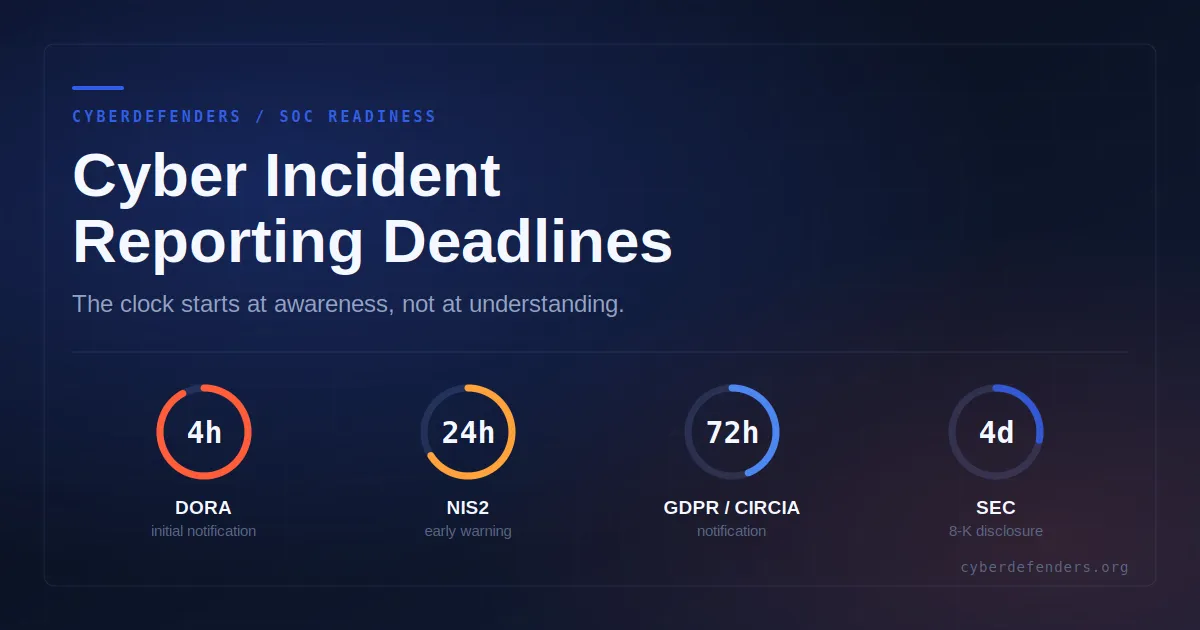
Cyber Incident Reporting Deadlines: What Your SOC Must Do (2026)
Cyber incident reporting deadlines are shorter than most security teams assume, and they start earlier. Four business days. That is how long a US public company has to disclose a material cyber inc...
How to Become a Digital Forensics Analyst: A 2026 Career Roadmap
You do not need a computer science degree, a law enforcement badge, or a decade in IT to become a digital forensics analyst. You need four things: solid operating system and networking fundamentals...
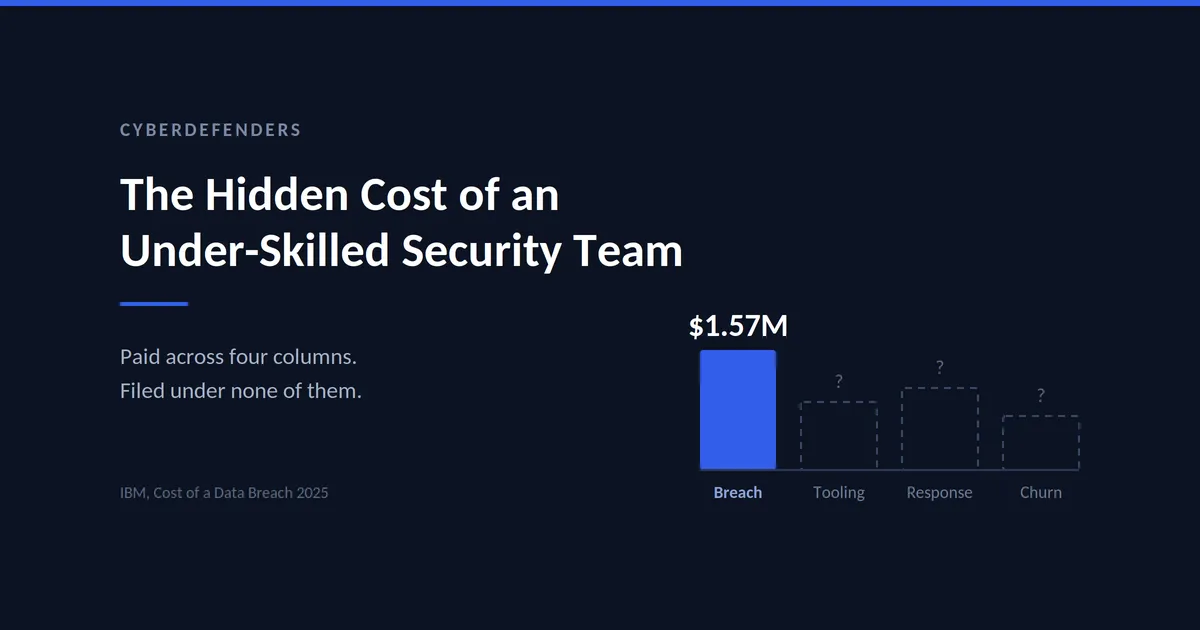
The Hidden Cost of an Under-Skilled Security Team
The costs of a security team that everyone can see are the ones on the budget: salaries, tooling, licenses, maybe a managed service. The cost nobody puts on a slide is the cybersecurity skills gap,...
Why Most SOC Analysts Fail Their First Real Incident Response
You hire a promising SOC analyst. They pass the certifications, clear 200 alerts a shift, and keep the queue clean. Then a real incident lands, and they freeze. If you own SOC readiness as a man...
MITRE ATT&CK Training: How to Turn Framework Knowledge Into Investigation Skills
The MITRE ATT&CK framework has become the shared language of cyber defense. Detection engineers map rules to it, threat intel teams profile adversaries with it, and CISOs report gaps to the boa...
CyberDefenders' participation in Locked Shield 2026
CyberDefenders Joins NATO CyberDefense Center for Locked Shields 2026 to Sharpen the Next Generation of Defenders Bridging the gap between modern cloud security training and real-world cyber def...
Fileless Malware Detection: How SOC Teams Hunt In-Memory Attacks
Fileless Malware Detection: How SOC Teams Hunt In-Memory Attacks Traditional malware detection relies on a simple principle: malware writes files to disk, antivirus scans those files, and signat...
Encoded PowerShell Detection:How to Investigate Encoded PowerShell Commands
How to Investigate Encoded PowerShell Commands: SOC Detection Guide PowerShell’s -EncodedCommand flag (aliases: -enc, -en) accepts a Base64-encoded UTF-16LE string and executes it at runti...
Azure Cloud Security: The SOC Analyst's Complete Detection & Threat Hunting Guide (2026)
Azure Cloud Security: The SOC Analyst's Complete Detection & Threat Hunting Guide (2026) Azure Cloud Security is not just a product suite; it is an operational discipline. Microsoft Azur...
Alert Triage Process: The Complete SOC Analyst's Guide
Alert Triage Process: The Complete SOC Analyst's Guide Alert triage is the structured process of receiving security alerts, evaluating them for legitimacy and severity, and determining the a...
Hacker Mindset: How Do Attackers Really Think?
Hacker Mindset: The SOC Analyst's Guide to Stopping Attacks Before They Happen The hacker mindset is not a skill set; it's a way of thinking. And if you work in a Security Operations Cen...
Disk Forensics: SOC Analyst Playbook
Disk Forensics for SOC Analysts: How It Informs Detection and Threat Hunting Disk forensics is no longer the exclusive domain of incident responders or law enforcement investigators. Modern SOC ...
Cross-Site Scripting (XSS): How the Browser Security Model Works and Why It Breaks
Cross-Site Scripting (XSS): How the Browser Security Model Works and Why It Breaks Cross-Site Scripting (XSS) is a web application vulnerability that allows attackers to inject malicious scripts...
SOC Simulator: USB Device Alert Investigation
USB Device Alert Investigation on a Corporate Endpoint A field guide for Tier 1 and Tier 2 SOC analysts covering removable media triage, evidence collection, insider risk signals, and malware de...